AgenticOS-C3 by PNN Solutions
AI Safety & Security Engineering Platform of SPE
Solve AI safety anxiety with quantifiable, automated security posture elevation. Secure your AI models, model usage, data, infrastructure, and governance with the advanced AI safety and security engineering platform. AgenticOS-C3 comes equipped with the Autonomous Security AI Agents & PNN LSP—an advanced LLM Security Posture Elevation engine ("LLM Wiz") designed to quantify, visualize, anticipate, simulate, and help neutralize AI threats. Complete the request form to engage.
Who May Engage PNN LSP & AgenticOS-C3 to Solve AI Safety Anxiety?
Types of institutions, industry leaders, and the strategic advantages of deploying PNN LSP & AgenticOS-C3 across every layer of the AI stack.
| Types of Institutions | Examples of Institutions | Why Engage PNN LSP and AgenticOS-C3? |
|---|---|---|
| Hardware Layer AI Infrastructure Providers |
Nvidia, AMD, Apple
Compute, GPU acceleration & specialized AI silicon chipsets. |
Harden Silicon & GPU Compute Integrity
Stress-test hardware roots of trust and firmware integrity against adversarial AI payloads; prevent supply-chain tampering and protect distributed accelerator clusters from catastrophic resource-exhaustion exploits. |
| Cloud Layer AI Cloud Providers |
AWS, Azure, Google Cloud
Managed hosting, model serving, and distributed AI cloud infrastructure. |
Defend Multi-Tenant AI Clouds at Scale
Proven architecture based on protecting 1,800+ clouds; deploy agentic defense swarms to isolate tenant workloads, prevent container/microVM breakouts, and enforce real-time Zero Trust boundaries across hybrid cloud fleets. |
| Model Layer Builders of LLMs |
OpenAI, Anthropic, Meta
Foundation model creators and frontier AI research labs. |
Automate Red Teaming & Security Posture Elevation
Execute probe-driven multi-agent adversarial red teaming (AosMythosSim); quantify alignment, prevent jailbreaks/DAN bypasses, and validate model safety against ~300 NIST/FedRAMP controls prior to production release. |
| Runtime Layer AI Application Builders |
CISOs, CTOs, DevSecOps, Red Teams
Enterprise engineering teams deploying agentic workflows and LLM applications. |
Deploy Runtime Guardrails & Agent Defenses
Eliminate prompt injection, data poisoning, and sensitive context leakage (PII/secrets) across RAG pipelines; equip DevSecOps and Red Teams with continuous, automated posture evaluation and active runtime intervention. |
| Governance Layer Government Regulators & Users |
NIST, DHS, DoD
Federal agencies, defense stakeholders, and standards-setting bodies. |
Verify Compliance & National Defense Readiness
Operationalize NIST AI RMF 600-1 and federal Zero Trust mandates; audit autonomous agent decision chains with decoupled canonical control planes, unified telemetry logging, and defense-grade posture assurance. |
Background: How to Protect 1800 Clouds to Save $35M?
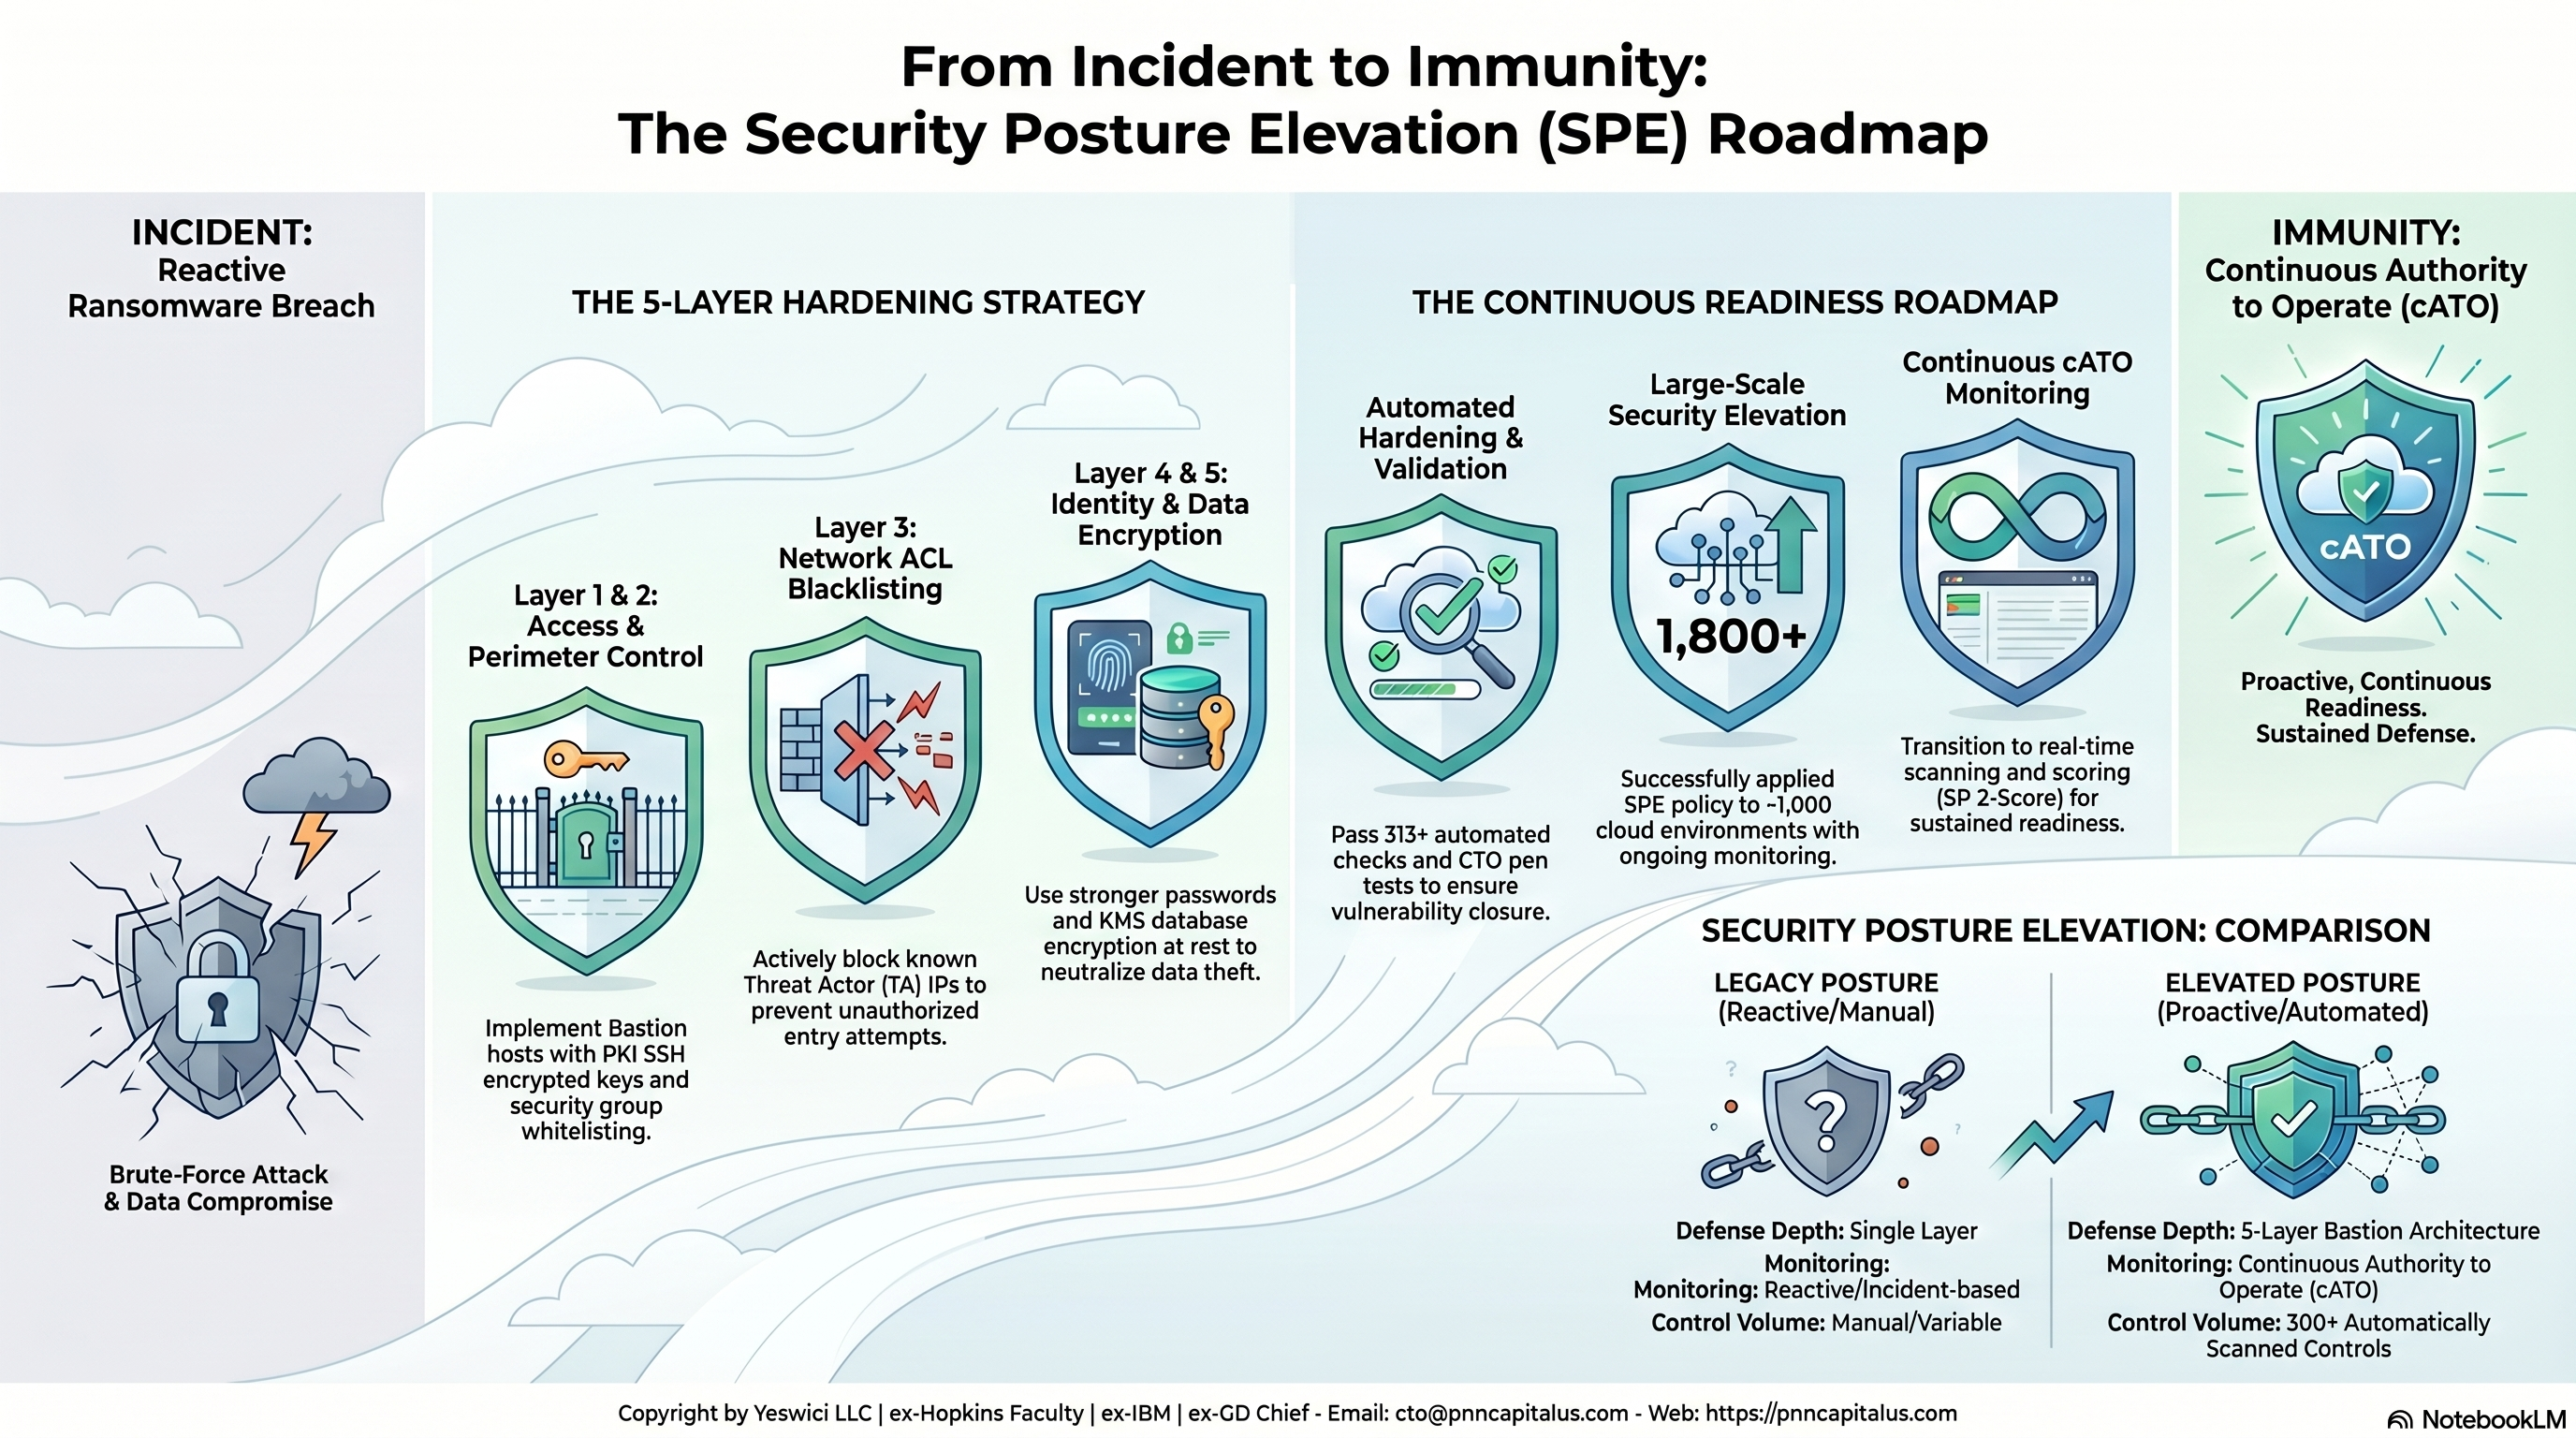
How to Elevate Security Posture by AgenticOS-C3 & Agentic Swarm?
Core Harness Architecture of AgenticOS-LSP & AgenticOS-Teams of the PNN SPE Roadmap:Demonstrating AgenticOS-C3 Autonomous Defense with Agentic Swarm
PNN Solutions to AI Safety & Security Engineering Problems
Autonomous defense, automated security posture evaluation, and standards-aligned protection across models, data, and infrastructure.
| Missions / Goals | AI Safety & Security Problems | PNN AgenticOS-C3 Solutions |
|---|---|---|
| Model Layer Securing AI Models | Jailbreaks (DAN, GCG), prompt injections, toxic outputs, hallucinations, backdoors, and the lack of automated, web-based posture assessments across local and cloud LLMs. |
PNN AgenticOS-LSP
Automated probe-driven security scans, multi-model adapter integration (Ollama, HuggingFace, Cloud APIs), pass/fail compliance dashboards, and assessment against ~300 NIST/FedRAMP controls. |
| Usage Layer Securing Model Usage | Runtime adversarial prompt hijacking, evasion through multi-turn conversational loops, unauthorized agent actions, and operational misuse bypassing static guardrails. |
PNN Mythos extensions, red team, and penetration tests
Autonomous threat simulation via AosMythosSim, multi-agent adversarial red teaming, real-time stress testing, and penetration testing against production LLM deployments. |
| Data Layer Securing the Data | Database leaks, chat history exposure, sensitive context leakage (PII/secrets), untrusted prompt injections targeting retrieval (RAG) datasets, and data poisoning. |
PNN SPE Roadmap
Zero Trust data access controls, context-window sanitization linters, PII detection filters, and hardened data isolation boundaries across multicloud and edge AI architectures. |
| Infra Layer Securing Infrastructure | GPU/compute resource exhaustion from adversarial payloads, sandbox and microVM breakout attempts, API abuse, and configuration drift across distributed hybrid clouds. |
AgenticOS-C3-Teams agentic swarm
Autonomous security agent swarms providing proactive perimeter defense, containerized worker sandboxing, real-time rate limiting, and auto-remediation across 1800+ clouds and edges. |
| Governance Layer Governance | Unverifiable agent decision chains, opaque model auditing, and inability to systematically validate compliance against NIST AI RMF 600-1 and federal standards. |
PNN SPE roadmap, PNN LSP, and core harness architecture
LLM security posture risk scores, decoupled canonical control planes (Policy, Execution, Verification, Delivery & Audit), centralized database/S3 telemetry logging, automated compliance scoring, and pluggable SIEM/GRC integrations. |
Complete the Request Form to Engage PNN LSP & AgenticOS-C3
Please provide your organization's details below to initiate an evaluation or security engagement.
Proposal and R&D in progress:
- AgenticOS-C3-Quantum: Quantum-resilient networks and AI-driven cybersecurity
- AgenticOS-C3-ZT: Real-time Zero Trust data access & control for multicloud networks
- AgenticOS-C3-SPE: implementation for hybrid multicloud and edge AI